
Organizations in Austin operate across SaaS, cloud infrastructure, APIs, enterprise applications, healthcare, financial services, technology, and other connected environments. As these attack surfaces grow, security testing needs to do more than identify vulnerabilities. It also needs to determine which weaknesses can actually be exploited.
Austin has an established cybersecurity ecosystem that includes specialized offensive security firms, penetration testing providers, security consultancies, and larger cybersecurity companies with a local presence. Providers differ in their testing methods, areas of expertise, and service coverage.
Organizations evaluating security testing companies should look beyond brand recognition and price. Key considerations include tester expertise, testing methodology, manual testing depth, attack-surface coverage, evidence quality, reporting, remediation support, retesting, industry experience, scalability, and overall fit.
How We Evaluate Security Testing Companies
There is no single security testing company that fits every organization’s requirement.
A SaaS company testing APIs and cloud-native applications can have very different needs from a healthcare organization, financial institution, government contractor, or enterprise testing a large internal network.
Instead of evaluating providers based only on company size or market visibility, consider the following factors:
- Tester expertise and practical experience
- Security testing methodology
- Manual versus automated testing depth
- Application, API, mobile, cloud, network, and infrastructure coverage
- Red team and adversarial testing capabilities
- Quality of vulnerability evidence
- Reporting and remediation guidance
- Retesting and fix validation
- Industry and regulatory experience
- Communication and collaboration
What to Look for in an Offensive Security Partner
Choosing an offensive security provider starts with understanding the organization’s attack surface and testing objectives.
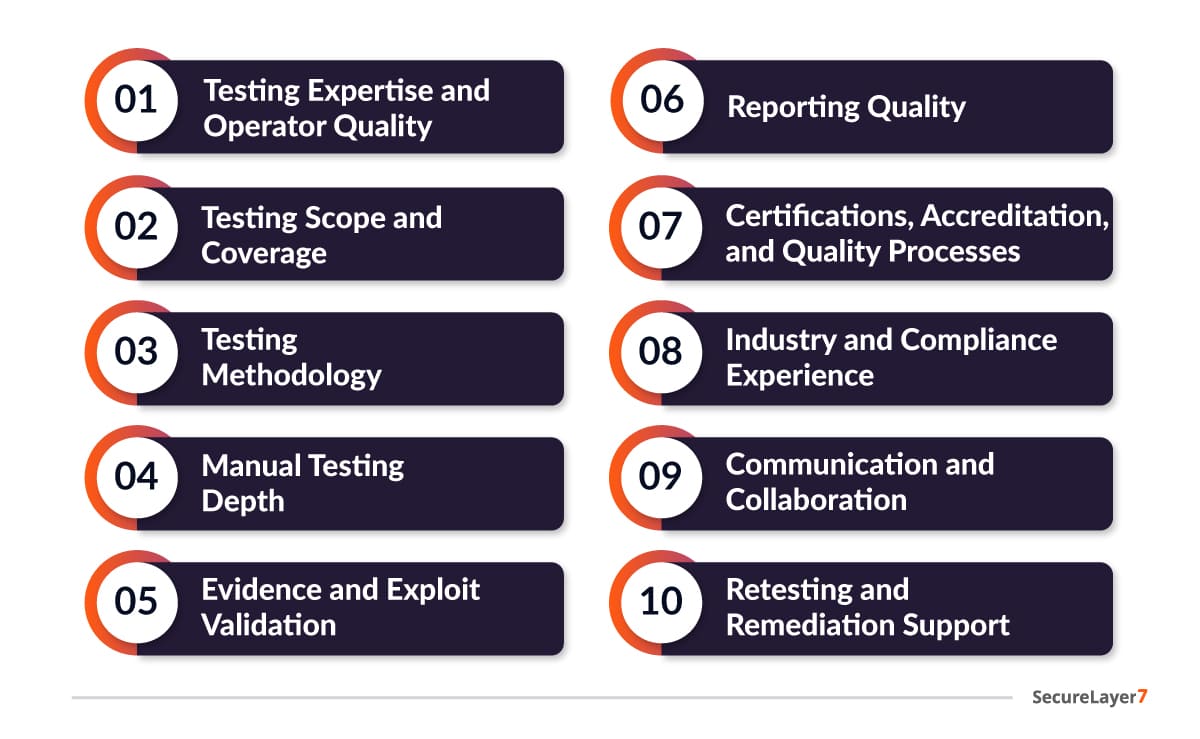
1. Testing Expertise and Operator Quality
The quality of an assessment depends heavily on the security professionals conducting the work.
Do not evaluate a provider only by its company name. Ask who will actually perform the engagement.
Consider:
- Practical offensive security experience
- Relevant technical certifications
- Application, API, cloud, mobile, or infrastructure specialization
- Red team experience
- Experience with the organization’s technology stack
- Technical research and vulnerability discovery experience
2. Testing Scope and Coverage
Determine the provider can assess the attack surfaces relevant to the organization.
These may include:
- Web applications
- APIs
- Mobile applications
- Cloud environments
- Networks and infrastructure
- Containers and Kubernetes
- IoT systems
- AI and LLM applications
- Identity infrastructure
3. Testing Methodology
Ask how the provider conducts an assessment from initial scoping through remediation.
A structured methodology can include:
- Scoping and rules of engagement
- Reconnaissance and attack-surface discovery
- Threat modeling
- Vulnerability discovery
- Manual validation
- Controlled exploitation
- Attack-path analysis
- Risk assessment
- Reporting
4. Manual Testing Depth
Automated scanning provides useful coverage for known vulnerabilities and common configuration issues, but it does not replace manual investigation.
Determine testers manually evaluate:
- Authentication
- Authorization
- Session management
- Business logic
- Privilege escalation
- API abuse
- Application workflows
- Vulnerability chaining
- Complex attack paths
5. Evidence and Exploit Validation
A useful finding should explain more than the existence of a vulnerability.
Look for:
- Reproducible evidence
- Proof-of-concept information
- Screenshots where relevant
- Request and response evidence
- Affected assets
- Exploit conditions
- Attack paths
- Technical impact
- Business impact
6. Reporting Quality
Request a sample report before selecting a provider.
A useful penetration testing report should contain:
- Executive summary
- Technical vulnerability descriptions
- Severity and risk context
- Evidence
- Reproduction information
- Business impact
- Remediation recommendations
- Affected assets
- Testing scope and methodology
7. Certifications, Accreditation, and Quality Processes
Relevant tester certifications and company-level accreditations can provide additional evidence of technical competency and established processes.
Certifications alone do not guarantee the quality of an engagement.
Organizations should evaluate credentials alongside:
- Testing methodology
- Tester experience
- Quality assurance processes
- Sample reports
- References
- Relevant case studies
8. Industry and Compliance Experience
Organizations operating in regulated environments should determine the provider has experience supporting applicable security requirements.
Examples can include:
- PCI DSS
- SOC 2
- ISO 27001
- HIPAA-related security requirements
- NIST frameworks
- Government security requirements
9. Communication and Collaboration
Security testing often requires communication before, during, and after an engagement.
Evaluate the provider offers:
- Clear scoping discussions
- Defined communication channels
- Testing progress updates
- Access to testers
- Critical-finding escalation
- Remediation discussions
- Post-engagement support
10. Retesting and Remediation Support
Testing does not necessarily end with the initial report.
Ask the engagement includes:
- Remediation guidance
- Tester clarification
- Fix validation
- Retesting
- Updated findings
- Closure documentation
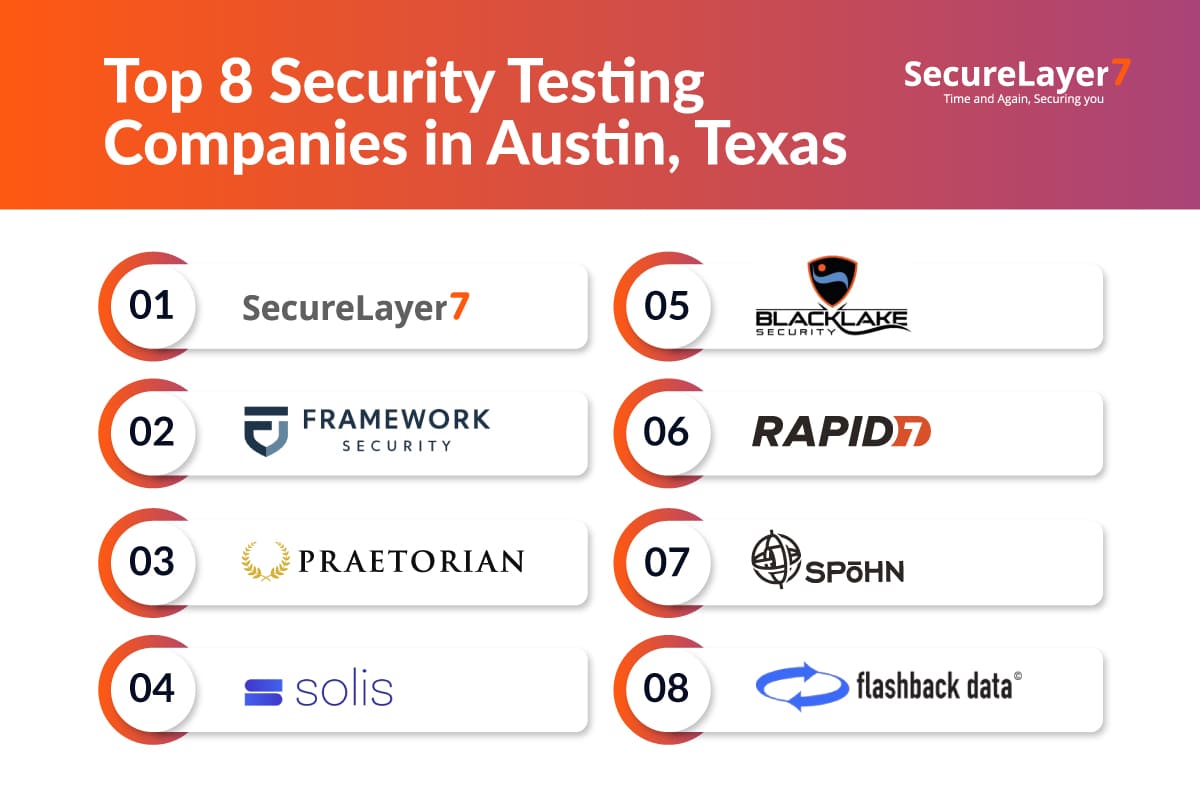
Top 8 Security Testing Companies in Austin, Texas
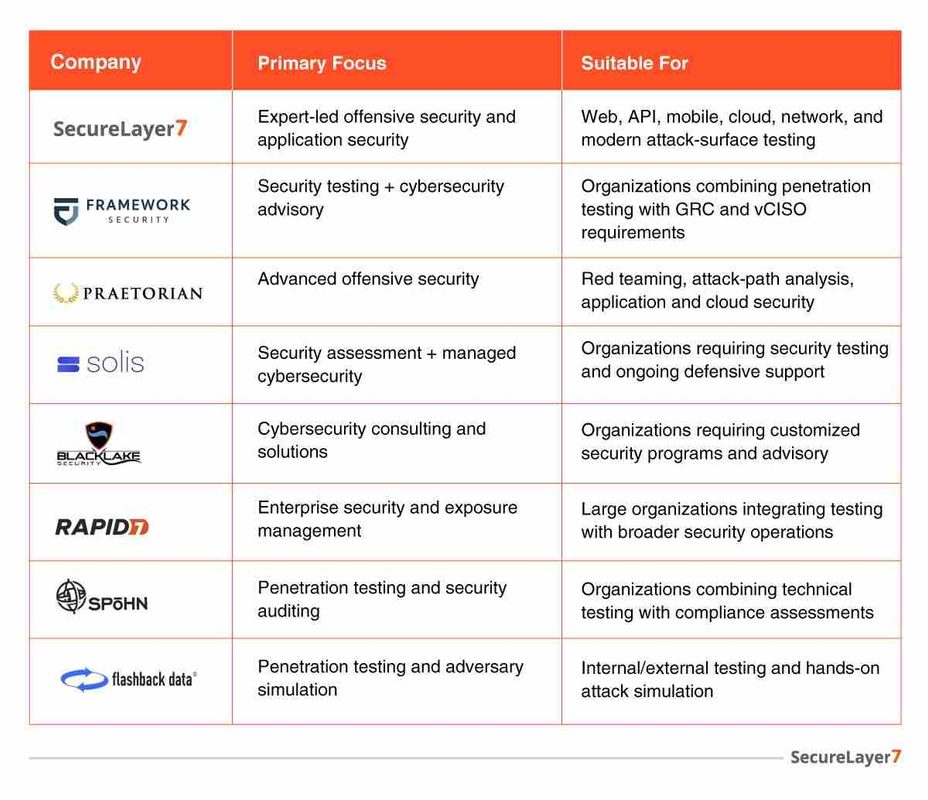
The following companies represent different approaches to security testing in the Austin market, ranging from specialized offensive security and penetration testing to broader cybersecurity consulting and exposure management.
The list considers factors such as Austin presence or service availability, security testing capabilities, methodology, attack-surface coverage, manual testing expertise, reporting, remediation support, and broader cybersecurity experience.
The appropriate provider depends on the organization’s attack surface, testing objectives, industry requirements, technical environment, and preferred engagement model.
1. SecureLayer7
SecureLayer7 is a globally recognized offensive security company specializing in application security, API security, cloud security, and red teaming. The company focuses heavily on modern attack surfaces such as APIs, microservices, and cloud-native environments, making it highly relevant for today’s digital-first organizations.
What differentiates SecureLayer7 is its research-driven testing approach combined with its BugDazz PTaaS platform, which enables continuous penetration testing, centralized reporting, and real-time collaboration. The company works with enterprises and high-growth startups across industries, delivering tailored security programs aligned with compliance and business risk.
SecureLayer7’s offerings are tailored to both enterprise-grade companies and SMEs, which is a big USP of the company.
Key Services
- Web application penetration testing
- API penetration testing
- Mobile application penetration testing
- Cloud penetration testing
- Network penetration testing
- Red team assessments
- Security testing for emerging attack surfaces
Certifications:
CREST accreditation, CERT-In, ISO 27001:2013, ISO 9001:2015
Compliance Reporting:
PCI-DSS, HIPAA, SOC II, ISO 27001
What it does well:
- Automatically discovers APIs, including shadow and undocumented endpoints
- Detects and blocks API attacks in real-time during live traffic
- Identifies sensitive data exposure, such as tokens and credentials
- Supports REST, SOAP, and gRPC across cloud and on-prem environments
- Integrates into CI/CD pipelines for continuous security testing
- Provides visibility into the overall API attack surface
2. Framework Security
Framework Security is an Austin cybersecurity company that combines penetration testing with broader cybersecurity consulting, compliance, risk management, and virtual CISO services.
Rather than focusing only on individual security assessments, its approach can support organizations that are building or improving broader cybersecurity programs.
Key Services
- Penetration testing
- Security assessments
- Risk assessments
- Cybersecurity consulting
- Virtual CISO services
- Compliance and security-program support
Testing Approach
Framework Security combines technical security assessment with governance, risk, compliance, and cybersecurity advisory capabilities.
3. Praetorian
Praetorian is an Austin-based offensive security company providing penetration testing, red teaming, application security, cloud security, product security, and continuous offensive security capabilities.
Its approach combines experienced security engineers with technology-assisted offensive security testing.
Key Services
- Application penetration testing
- Network penetration testing
- Cloud security testing
- Red teaming
- Product security
- Attack-surface assessment
- Continuous offensive security
Testing Approach
Praetorian focuses on attacker-driven security assessment and identifying exploitable attack paths rather than treating vulnerabilities only as isolated findings.
4. Solis Security
Solis Security provides cybersecurity services spanning security assessments, managed cybersecurity, incident response, and security advisory capabilities.
Its combination of proactive and defensive services makes it different from providers focused exclusively on penetration testing.
Key Services
- Security assessments
- Managed cybersecurity
- Incident response
- Security consulting
- Cyber risk support
Testing Approach
Solis combines security assessment capabilities with incident-response and ongoing cybersecurity support.
5. BlackLake Security
BlackLake Security is headquartered in Austin and provides cybersecurity consulting and security solutions tailored to different organizational requirements.
Its broader consultative approach makes it relevant for organizations looking beyond a standalone penetration test toward security architecture and security program requirements.
Key Services and Capabilities
- Cybersecurity consulting
- Security architecture
- Risk-focused cybersecurity services
- Security technology solutions
- Security-program support
Testing Approach
BlackLake emphasizes understanding an organization’s existing environment and security requirements before recommending appropriate security solutions and services.
6. Rapid7
Rapid7 provides cybersecurity technology and services across vulnerability management, exposure management, threat detection, incident response, and penetration testing.
Its security testing capabilities are part of a broader enterprise cybersecurity ecosystem.
Key Services
- Penetration testing
- Vulnerability management
- Exposure management
- Managed detection and response
- Incident response
- Security analytics
Testing Approach
Rapid7 combines security services with platform-based vulnerability, exposure, and threat-management capabilities.
7. Spohn Security Solutions
Spohn Security Solutions operates from Austin and provides penetration testing, security assessments, compliance audits, and related cybersecurity services.
Its security practice emphasizes customized assessments rather than applying the same testing scope to every organization.
Key Services
- Penetration testing
- Security assessments
- IT security audits
- HIPAA security risk assessments
- Social engineering testing
- Compliance-related security assessments
Testing Approach
Spohn combines hands-on security assessment with audit and compliance expertise. Its penetration testing services can be tailored to an organization’s infrastructure and security requirements.
8. Flashback Data
Flashback Data operates its main office in Austin and provides penetration testing and ethical hacking services alongside its broader data and cybersecurity capabilities.
Its penetration testing approach includes internal and external assessments, adversary simulation, and social engineering.
Key Services
- Penetration testing
- Internal penetration testing
- External penetration testing
- Ethical hacking
- Adversary simulation
- Social engineering
Testing Approach
Flashback Data emphasizes hands-on penetration testing designed to identify complex and multi-step vulnerabilities rather than relying only on automated scanning.
Its assessments can be customized based on the organization’s infrastructure, attack surface, and security objectives.
Quick Comparison of Austin Security Testing Companies
Conclusion
Organizations should evaluate the actual testing team, methodology, manual testing depth, attack-surface coverage, vulnerability evidence, reporting quality, remediation support, retesting, industry experience, security practices, scalability, and overall value.
Austin organizations can choose from specialized offensive security firms, broader cybersecurity consultancies, and enterprise security providers. The right fit depends on the organization needs application penetration testing, API security testing, cloud assessments, red teaming, network testing, continuous offensive security, or broader security program support.
SecureLayer7 provides expert-led penetration testing for web applications, APIs, mobile applications, cloud environments, networks, and other modern attack surfaces, with an Austin U.S. delivery presence. Organizations considering SecureLayer7 should evaluate its methodology, tester expertise, evidence, reporting, remediation support, and retesting against the same criteria used to assess other providers.
Connect with SecureLayer7 to assess your security risks, identify exploitable vulnerabilities, and strengthen your security defenses.
Frequently Asked Questions(FAQs)
Evaluate tester expertise, methodology, manual testing depth, relevant attack-surface coverage, evidence quality, reporting, remediation support, retesting, industry experience, confidentiality controls, scalability, and overall value.
No. Vulnerability scanning primarily uses automated tools to identify known vulnerabilities and configuration issues. Penetration testing adds human analysis and controlled exploitation to investigate exploitability, business logic, authorization controls, attack paths, and security impact.
Relevant certifications depend on the engagement. Organizations can consider recognized offensive-security credentials and company-level accreditations alongside practical tester experience, methodology, quality-assurance processes, sample reports, and previous engagement experience.
Local presence can provide advantages such as time-zone alignment, easier communication, local contracting, and support for engagements requiring on-site activity. Organizations should also consider whether the provider has the technical specialization required for the systems being tested.
Review whether the report contains clear vulnerability descriptions, technical evidence, affected assets, exploitability information, business impact, reproduction details, severity, and actionable remediation guidance.

