What is Role-Based Access Control (RBAC)?
Role-based access control (RBAC) is an access management model that determines which systems, applications and data users can access based on their assigned roles. For example, a security analyst might have permission to configure firewalls but not access customer records.
Similarly, a sales representative, meanwhile, might be able to view customer accounts but not modify firewall settings.
In an RBAC system, administrators assign one or more roles to each user and each role defines a specific set of permissions that determines which resources a user can access and what actions they can perform.
These permissions typically reflect job responsibilities. A finance role might allow employees to process purchases, run financial forecasts or access supply chain systems. An HR role might provide access to personnel records and employee benefits applications.
Organizations with large workforces often use role based access control to simplify access management and protect sensitive information across their digital environments. The model can also govern access to physical resources, such as electronic locks securing office buildings, restricted areas and data centers.
By limiting access to the resources required for each role, RBAC helps reduce the risk of unauthorized access, insider threats, accidental data exposure and misuse of compromised accounts.
Why It Matters
In enterprise and cloud-driven ecosystems, RBAC plays a critical role in maintaining both security and operational efficiency.
- Cloud Security: In cloud infrastructures like AWS, Azure, or Google Cloud, RBAC integrates directly with Identity and Access Management cloud security policies to control resource-level access.
- Enterprise IT Systems: Large organizations often manage thousands of users across multiple departments, applications, and data repositories. RBAC helps enforce consistent access policies across all systems, making it easier to onboard, transfer, or offboard employees without manual reconfiguration.
- SaaS Platforms: For Software-as-a-Service (SaaS) applications, RBAC provides a foundation for multi-tenant security. By defining roles such as Admin, Editor, or Viewer, SaaS providers can ensure customers manage access within their teams efficiently and securely.
How Does RBAC Work?
Role-Based Access Control (RBAC) manages user access by assigning permissions according to predefined roles. Instead of granting access to each user individually, organizations define roles with specific permissions and assign users to the roles that match their job responsibilities.
For example, consider a hotel that uses keycards to control access to its rooms. Guests receive keycards that open only their assigned rooms, housekeeping staff can access rooms on designated floors, and maintenance workers may have access to doors throughout the building.
Although everyone uses the same type of keycard, the level of access depends on their assigned role.
Organizations can further simplify RBAC by grouping users according to their job functions or responsibilities.
Administrators assign permissions to these groups rather than managing each user separately. When employees join a group or move to another one, their access rights change accordingly, making permission management easier to maintain as the organization grows.
Key Components of RBAC
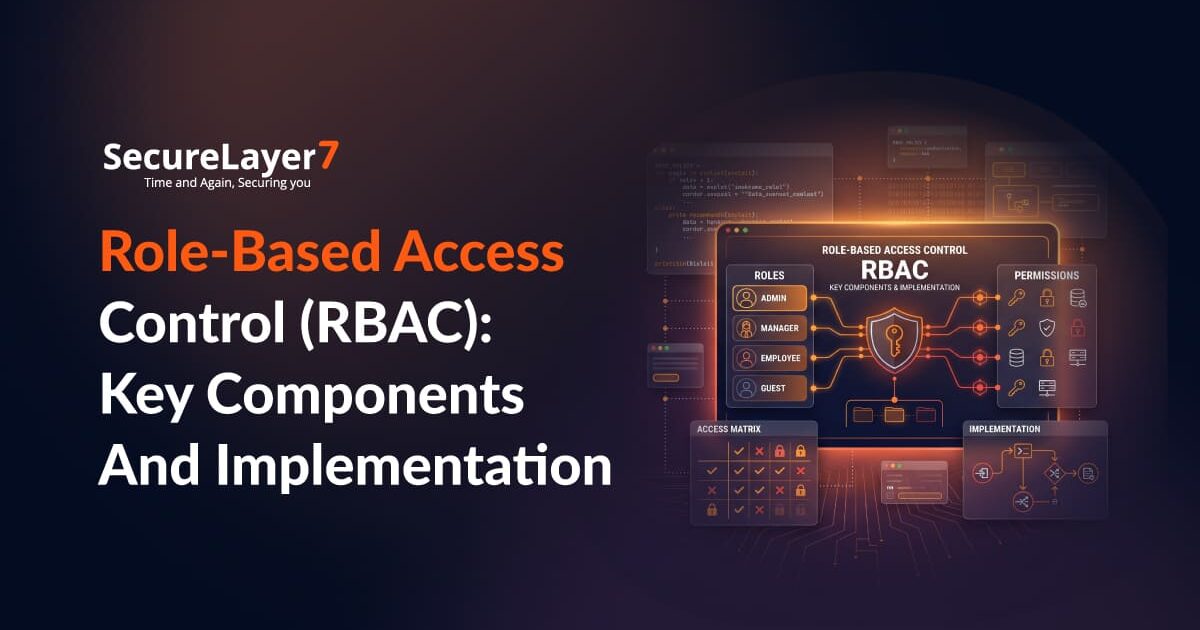
RBAC relies on four core components: users, roles, permissions, and sessions. Together, they determine who can access a system, which actions they can perform, and how their access is managed.
Users: Identities Assigned Roles
Users are the identities that receive role assignments within an RBAC system. Each user may be assigned one or more roles based on their responsibilities and authorized access requirements.
For example, an HR executive may be allowed to view employee records but not access financial reports. Instead of assigning permissions individually, administrators can grant the appropriate role to manage access more consistently.
Roles: Groups of Related Permissions
A role represents a job function or responsibility and is associated with a defined set of permissions. Common examples include System Administrator, Finance Manager, and Customer Support Agent.
When an administrator assigns a role to a user, the user receives the permissions associated with that role, subject to the system’s access policies. Well-defined roles simplify onboarding, support consistent access management, and make it easier to adjust permissions when responsibilities change.
Permissions: Actions Allowed on Resources
Permissions specify which operations a user can perform on a particular resource. These operations may include viewing records, editing data, creating entries, deleting files, or approving transactions.
For example:
- A finance manager may have permission to approve invoices but not modify payroll records.
- A Sales Representative may be allowed to update customer information but not change pricing policies.
By associating permissions with roles, RBAC helps organizations enforce access restrictions consistently.
Sessions: Activating Roles During Access
A session represents a user’s active interaction with a system. In the formal RBAC model, a user can activate a subset of the roles they are authorized to hold during a session, subject to applicable constraints and policies.
For example, an employee assigned both Analyst and Reviewer roles may activate the appropriate role for a particular task, if the system supports this functionality. Separation-of-duties rules can restrict the simultaneous activation of conflicting roles.
Session management, combined with appropriate audit logging, helps organizations enforce access policies and maintain accountability for user activity.
Examples of RBAC
Organizations can assign access permissions to users individually or through predefined roles and groups. When an administrator adds a user to a role group, the user inherits the permissions associated with that group, allowing access to the tools and resources required for their responsibilities.
Organizations can define roles for administrators, employees in specific job functions, and external users such as guests. For example:
- Software Engineer: Receives access to development tools such as GitHub, Docker, and Jenkins, without unnecessary permissions to unrelated business systems.
- Marketing Specialist: Can access marketing resources, including email marketing lists, Google Analytics, and company social media accounts.
- Human Resources Employee: Gets access to HR platforms such as ADP, Oracle Cloud Human Capital Management, or Paycor to manage employee records and related processes.
Common Challenges in Implementing RBAC
Implementing RBAC is one of the most effective ways to strengthen an organization’s security posture and streamline access management.
The process is not without obstacles. Many organizations encounter challenges, such as excessive role creation, poor planning, and integration difficulties, which can undermine the intended benefits. Below are the most common pitfalls and how to overcome them.
1. Role Explosion
The most frequent problem in RBAC deployments is role explosion, the uncontrolled growth of roles across departments and business units. Similar roles with minor variations lead to complexity, duplication, and administrative burden.
Why it’s a challenge:
- Difficult to maintain and audit hundreds of overlapping roles.
- Increases risk of granting unnecessary permissions.
- Makes it hard to implement consistent governance.
2. Poor Initial Mapping of Roles and Permissions
RBAC depends heavily on accurately defining what each role can and cannot do. A poor or incomplete mapping between roles and permissions leads to confusion, security gaps, or overly restrictive access that impacts productivity.
Why it’s a challenge:
- Misaligned access privileges expose sensitive data.
- Overly restrictive permissions disrupt workflows.
- Manual adjustments create long-term inconsistencies.
3. Lack of Regular Audits Leading to Privilege Creep
Without periodic reviews, users often accumulate permissions as they move between roles or projects – known as privilege creep. This undermines the principle of least privilege and increases the attack surface.
Why it’s a challenge:
- Violates data protection frameworks such as GDPR, HIPAA, and SOC 2.
- Allows inactive or over-privileged accounts to remain active.
- Increases risk of insider threats and compliance violations.
4. Integration Complexity with Legacy Systems
Older applications often lack support for centralized identity management, making RBAC implementation more complex. Integrating modern IAM solutions with legacy systems can require custom connectors or middleware.
Why it’s a challenge:
- Slows down deployment timelines.
- Leads to inconsistent access enforcement across systems.
- Creates blind spots that weaken overall security.
5. Resistance to Change During Migration
Transitioning to RBAC often means redefining long-standing access patterns and restricting broad privileges. Employees accustomed to unrestricted access may perceive the change as inconvenient, leading to pushback.
Why it’s a challenge:
- Reduces user adoption and cooperation.
- May encourage insecure workarounds or shadow access.
Implementing RBAC: A Step-by-Step Guide
Implementing Role-Based Access Control involves more than assigning roles and configuring permissions. Organizations need to identify who requires access, define appropriate roles, and review permissions regularly to ensure they remain aligned with job responsibilities.
A structured implementation process helps businesses manage access efficiently while reducing security risks.
1. Inventory Identities, Systems, and Critical Assets
Before designing an RBAC model, identify the users, systems, and resources that need protection. This inventory provides a clear picture of who accesses organizational systems and which assets require the strongest safeguards.
- Identify user types: Include employees, contractors, business partners, service accounts, automated integrations, and AI agents that interact with organizational systems.
- List systems and applications: Document business applications such as ERP, CRM, and HRIS platforms, along with cloud accounts, databases, Kubernetes clusters, collaboration tools, and specialized systems such as payment gateways.
- Identify critical assets: Determine which resources would cause the greatest damage if compromised, including sensitive customer data, intellectual property, production systems, and backups.
Small businesses may be able to manage this inventory using a spreadsheet, while larger organizations may need collaboration between IT, security, and business teams.
IAM and Identity Governance and Administration (IGA) platforms can help centralize identity and access information.
2. Define Role Scope and Naming Conventions
Once the inventory is complete, define what each role represents and establish consistent naming conventions. Clear role definitions make permissions easier to assign, review, and maintain.
Organizations can create roles based on different criteria:
- Job function: Sales Representative, Customer Support Tier 1, or Billing Specialist.
- Technical environment: Production Database Read-Only, Staging Deployment, or DevOps Observer.
- Specific responsibilities: Finance Accounts Payable Approver or HR Compensation Analyst.
Smaller organizations may need only a handful of roles, while enterprises may require hundreds to accommodate different departments, applications, and responsibilities.
The goal is to create enough roles to meet business requirements without introducing unnecessary complexity.
Organizations should also distinguish between global roles, such as Employee or Manager, and application-specific roles, such as CRM Administrator. This helps prevent users from receiving broader access than their responsibilities require.
3. Design Roles Using Top-Down and Bottom-Up Analysis
Effective RBAC design requires an understanding of both business requirements and existing access patterns. A top-down approach identifies the permissions users need to perform their jobs, while a bottom-up approach examines existing assignments to identify overlapping permissions, unnecessary privileges, and exceptions.
Work with department heads, application owners, and IT teams to determine:
- Which tasks employees need to perform in each role.
- Which resources they must view, create, modify, or delete.
- Which sensitive operations require additional approvals or restrictions.
At the same time, review existing permissions to identify users with similar access requirements and accounts with excessive privileges. A senior job title, for example, should not automatically grant unrestricted access to every business system.
Use these findings to define roles, document their associated permissions, and establish separation-of-duties (SoD) requirements. Start with common roles, such as Employee, Manager, and IT Administrator, before introducing more specialized roles where necessary.
4. Implement Roles in IAM Platforms and Applications
After defining the roles, configure them within the organization’s identity infrastructure and applications. The objective is to ensure that users receive the appropriate permissions across the systems they need to access.
- Central directory or identity provider (IdP): Create and manage role-based groups through platforms such as Okta or Microsoft Entra ID.
- Application-level roles: Map central groups to application-specific roles, such as Administrator, Editor, or Viewer. Where supported, use SCIM or provisioning APIs to automate account creation and permission updates.
- Infrastructure access controls: Configure corresponding permissions in cloud platforms, databases, and Kubernetes environments using their native IAM or RBAC mechanisms.
Smaller organizations may implement RBAC by mapping identity provider groups to roles across their SaaS applications. larger enterprises may use IGA platforms to coordinate role assignments, approvals, and access reviews across multiple systems.
5. Migrate Users Gradually and Validate the Impact
Rolling out RBAC gradually helps organizations identify access issues before applying the model across the entire environment. A sudden change to existing permissions can disrupt workflows or prevent employees from accessing systems required for their jobs.
A phased implementation should include the following steps:
- Start with a pilot: Select a business unit or a limited set of applications, implement the proposed roles, and evaluate the results before expanding the rollout.
- Test before enforcement: Where supported, use simulation or audit-only modes to identify which access requests would be allowed or denied under the proposed configuration.
- Communicate changes: Inform employees about changes to their access rights and explain how they can request additional permissions when needed.
Collect feedback from users, administrators, and application owners to identify missing permissions, excessive access, and unexpected disruptions. Use these findings to refine role definitions before expanding the deployment.
RBAC should also become part of employee onboarding and offboarding. New employees should receive the roles required for their responsibilities, while departing employees should have their access revoked promptly.
6. Establish Governance, Reviews, and Lifecycle Management
RBAC is not a one-time configuration. As employees change positions and business requirements evolve, organizations must regularly review roles and permissions to prevent outdated access from creating security gaps.
Long-term RBAC governance should focus on three areas:
- Access reviews: Periodically review role assignments with managers and application owners. Pay particular attention to excessive privileges, inactive accounts, exceptions, and permissions that no longer match job responsibilities.
- Identity lifecycle management: Automate role assignments and removals through joiner-mover-leaver processes. When an employee changes departments, remove roles that are no longer required instead of simply adding new permissions.
- Exception management: Establish a process for granting temporary or unusual access. For example, an engineer investigating a production issue may receive elevated privileges for a limited period, subject to approval and automatic expiration.
Logging and reporting provide additional visibility into role assignments, permission changes, approvals, and access activity. These records help security teams investigate suspicious behavior, demonstrate compliance, and identify access that no longer meets business requirements.
By regularly reviewing permissions and automating access management wherever possible, organizations can keep RBAC aligned with the principle of least privilege while reducing administrative overhead and the risk of unauthorized access.
Conclusion
Role-Based Access Control (RBAC) stands out as a reliable framework for managing user access efficiently. By granting permissions based on roles instead of individuals, RBAC helps organizations strengthen security, prevent unauthorized access, and streamline user management.
As enterprises continue to adopt cloud and hybrid environments, RBAC provides a strong foundation for Zero Trust architecture and scalable identity management.
At SecureLayer7, we specialize in helping organizations design and implement robust access control and identity management (IAM) frameworks. Our experts can assess your current security posture, identify access gaps, and build customized RBAC strategies that align with your business goals.
To build a secure and compliant access control framework tailored to your business needs, Partner with SecureLayer7 – your trusted expert in access control, IAM, and cybersecurity solutions.
Frequently Asked Questions ( FAQs)
<!– wp:shortcode –>
Role-Based Access Control (RBAC) grants permissions according to a user’s assigned role, while Attribute-Based Access Control (ABAC) evaluates additional attributes to determine whether access should be allowed. These attributes may include a user’s security clearance, the requested action, the resource being accessed, or contextual factors such as the time of day and physical location. For example, RBAC might allow a Finance Manager to access financial reports based on their role. ABAC could further restrict that access to approved devices or specific working hours.
The primary difference lies in how access decisions are made. RBAC assigns permissions based on predefined user roles, whereas rule-based access control uses specific rules or conditions to allow or deny access. For example, a network security rule might block all traffic directed to a particular port, regardless of the user or application initiating the request. RBAC, by contrast, determines which resources and operations a user can access based on their assigned role.
A permission is an authorization to perform a specific action on a resource, such as downloading a file, modifying a record, or approving a transaction. In an RBAC system, permissions are associated with roles, and users receive those permissions through their role assignments. For example, an internal employee assigned a role with file-download privileges can download authorized documents, while an external user assigned a more restrictive role may be denied that capability.
